AI Enabled AutonomousCyber Defence Centre
An AI native SOC delivering continuous threat detection, intelligent response, and live cyber defense across enterprise environments.
24/7
Continuous Protection
Built for Modern Security Teams
As enterprises expand across cloud, hybrid, and on premises environments, traditional SOCs struggle to scale. Zayani Infosec AI Defence Centre centralizes telemetry, automates decision making, and reduces analyst fatigue, giving your security team intelligence and speed.
New to SOCs? Read our guide: What is a security operations centerReduction in False Positives
AI driven correlation eliminates alert noise and analyst fatigue.
Mean Time to Detect (MTTD)
Real time behavioral analytics identify threats instantly.
Lower SOC Operational Cost
Automation reduces reliance on large analyst teams.
Unified Security Command Center
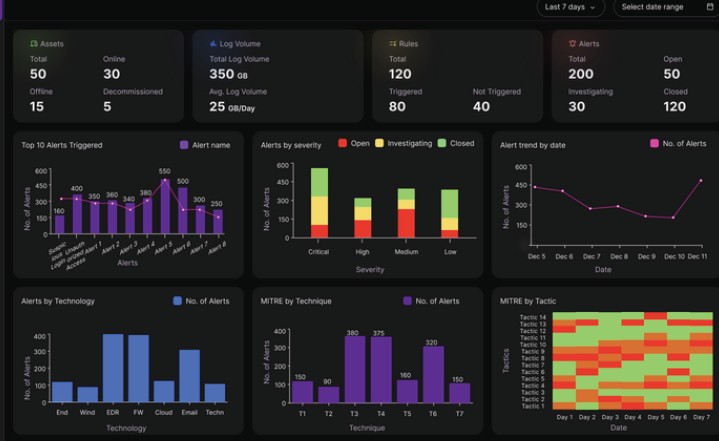
Monitor threats, analyze patterns, and respond to incidents from a single, intelligent dashboard. Our AI powered interface provides complete visibility across your entire security landscape.
- Real time asset monitoring and log volume tracking
- Alert severity classification with automated triage
- MITRE ATT&CK framework mapping for threat analysis
- Trend analysis and predictive threat intelligence
AI Driven Security Lifecycle
A continuous, AI driven security lifecycle that detects threats, prioritizes risk, and responds in real time, with human oversight where it matters.
Signal Ingestion
Telemetry collected from endpoints, network, cloud, identity, email, and applications.
AI Correlation & Analysis
Agentic AI correlates events, removes noise, and identifies real threats.
Risk Prioritization
Threats are scored based on impact, exploitability, and business context.
Automated Response
Playbooks trigger containment actions while notifying SOC analysts.
AI SOC Core Capabilities
Advanced AI powered capabilities designed to detect, investigate, and respond to cyber threats across cloud, hybrid, and on premises environments.
Cloud & Hybrid Monitoring
Continuous visibility across AWS, Azure, GCP, and hybrid infrastructures.
Threat Intelligence Fusion
AI enriches alerts using global threat feeds and behavioral context.
Identity & Access Protection
Detects anomalous login behavior, privilege misuse, and insider threats.
Endpoint & Network Security
Monitors endpoints, servers, and network traffic in real time.
AI Driven Alert Triage
Automatically prioritizes critical threats and suppresses false positives.
Automated Incident Response
Executes containment actions while keeping analysts in control.
Who Benefits from AI SOC
Designed for organizations that require scalable, intelligent, and continuous security without expanding analyst headcount.
Enterprise Security Teams
Reduce alert fatigue, accelerate investigations, and improve SOC efficiency.
Cloud First Organizations
Gain unified security visibility across dynamic cloud and hybrid environments.
Compliance Driven Industries
Support regulatory requirements with continuous monitoring and reports ready for audit.
Strengthen Your SOC Operations
Move from alert driven security to intelligent, automated defense powered by AI.